Email authentication is a set of DNS records (SPF, DKIM, and DMARC) that prove messages claiming your domain actually came from servers you authorize. Without that proof, Gmail and Yahoo treat bulk mail as untrusted.
I've watched open rates collapse overnight while teams rewrote subject lines for weeks. In those cases, the real break was a missing include, a shared DKIM domain, or no DMARC record at all.
If you send more than 5,000 messages per day to Gmail accounts, Google's Email sender guidelines require SPF and DKIM, a DMARC record (policy may stay at p=none), and From-domain alignment. Yahoo's Sender Best Practices set the same bulk-sender bar.
Below, I'll show you what each of the three records does, what Gmail and Yahoo check for, and how to set them up step by step. You'll also see the mistakes I still find most often, so you can rule them out before you touch another subject line.
Let's start with what email authentication actually is.
In this article
- What email authentication is
- Why Gmail and Yahoo care in 2026
- SPF: who may send for your domain
- DKIM: the signature that travels with the mail
- DMARC: policy, reports, and alignment
- BIMI after enforcement
- How to set up authentication step by step
- Common mistakes I still see
- FAQ
- Final Thoughts
What email authentication is
Anyone can type From: nike@nike.com into a header. Authentication is how receiving servers check whether Nike (or you) actually authorized that send.
Think of the stack as a passport check at the inbox door.
SPF is the guest list. DKIM is the wax seal, and DMARC is the bouncer's written instructions when either check fails.
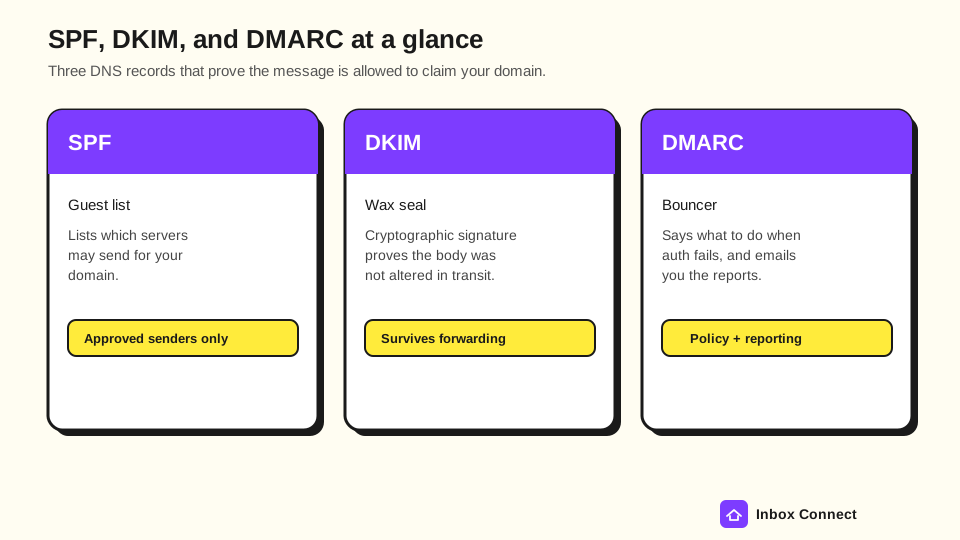
| Protocol | What it does | Simple analogy |
|---|---|---|
| SPF | Lists which servers may send mail for your domain | Guest list at the door |
| DKIM | Signs the message so tampering shows up | Wax seal on a letter |
| DMARC | Says what to do on failure and emails you reports | Bouncer policy + logbook |
Authentication does not fix bad list hygiene or boring content by itself. It removes the "this might be forged" reason providers fold you to spam first.
Pro tip: When I audit a domain and auth is Fail, I park subject-line tests. Creative work cannot rescue a From domain that fails alignment.
Why Gmail and Yahoo care in 2026
Bulk-sender rules that started in 2024 still shape every serious program in 2026. If you cross 5,000 messages in a day to personal Gmail accounts, you are a bulk sender under Google's definition.
Google asks bulk senders for SPF and DKIM, a published DMARC record, valid forward and reverse DNS (PTR), TLS, RFC 5322 formatting, From alignment with SPF or DKIM, and one-click unsubscribe on marketing mail. Yahoo expects SPF and DKIM, DMARC at least at p=none, alignment, low spam complaints, and easy unsubscribe.
Google also asks you to keep Postmaster Tools spam rates below 0.3% and ideally under 0.1%. Parking at 0.3% or higher blocks mitigation help until you stay under that ceiling for seven straight days.
Even if you send under the bulk threshold, publishing all three records still improves trust. Providers prefer authenticated mail over "From whoever" traffic.
Authentication is one part of inbox placement, and my guide on how to improve email deliverability and avoid spam covers the rest. Here, the focus stays on the three records so you can ship them without guessing.
SPF: who may send for your domain
SPF (Sender Policy Framework) is a TXT record that lists every server allowed to send mail on behalf of your domain. When a message arrives, the receiver checks whether the sending IP is covered by that list.
If the sending server is missing, the check fails. That looks like spoofing even when the tool is a survey app you forgot about.
A typical record looks like this:
v=spf1 include:_spf.google.com include:sendgrid.net ~all
That line says Google Workspace and SendGrid may send. Everyone else should be treated as suspicious (~all soft-fail; -all hard-fail).
Klaviyo works differently, so you will not find a Klaviyo include here. You connect a branded sending domain, and the DNS records it generates take care of SPF and DKIM on that subdomain.
A missing branded sending domain is the first gap I look for when I take on a Klaviyo agency account. Without it, you're sending from a shared Klaviyo domain and inheriting a reputation you didn't build.
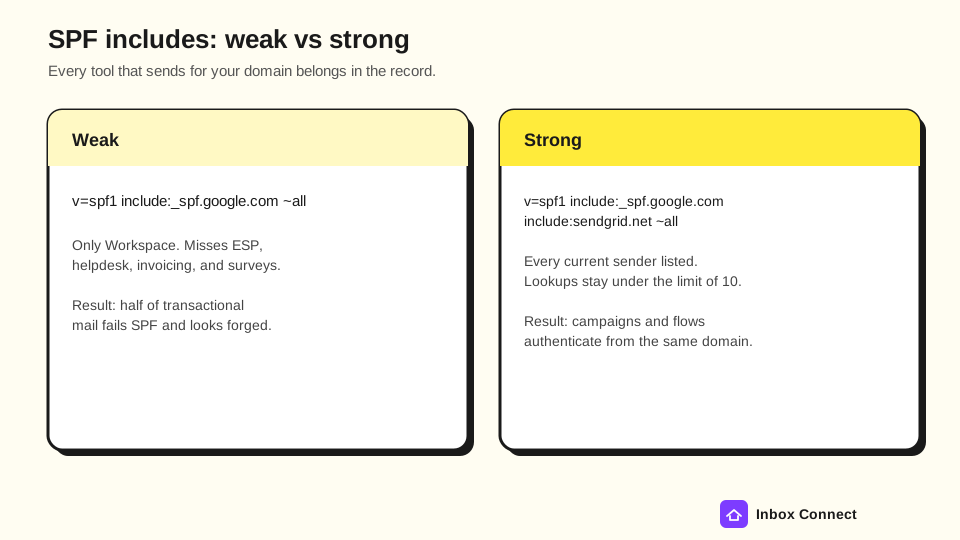
Weak vs strong SPF includes
Weak: v=spf1 include:_spf.google.com ~all after marketing moved to a new ESP last quarter. Helpdesk, invoicing, and the booking tool still send from the same From domain with no include.
Strong: One SPF record that lists every current sender, stays under the 10-DNS-lookup limit, and drops dead ESPs you stopped using years ago.
SPF limits you should respect:
- 10 DNS lookups max: Each
include:can nest more lookups. Over 10 and SPF fails hard. - Envelope sender only: SPF does not authenticate the visible From header by itself.
- Forwarding breaks SPF: Relayed mail often fails SPF even when it is legitimate.
Pro tip: Before you add another SaaS that "just sends receipts," run the free SPF checker. Count lookups first so the new include does not tip you over 10.
Those receipt tools are worth sending from their own subdomain, too, so a bad marketing week can't drag down order confirmations. My transactional email best practices guide covers how to split the streams.
SPF alone is not enough, so you need DKIM too.
DKIM: the signature that travels with the mail
DKIM (DomainKeys Identified Mail) adds a cryptographic signature to message headers.
Your sending system signs with a private key, and receivers verify with the public key you publish in DNS under a selector like k1._domainkey.yourdomain.com.
A passing signature proves two things: someone with your private key sent the message, and the signed parts were not altered in transit.
Google requires a DKIM key of at least 1024 bits for personal Gmail and recommends 2048 bits when your DNS provider supports it. Yahoo likewise expects DKIM on bulk mail with a solid key length.
Why DKIM often matters more than SPF on the wire
Forwarding routinely breaks SPF. The DKIM signature rides with the message, so alignment can still pass DMARC after a forward when DKIM is intact.
That is exactly why providers want both protocols live.
Weak vs strong DKIM setup
Weak: You send from the ESP's shared domain because "it worked out of the box." You are borrowing their reputation. When you leave that ESP, you start from zero.
Strong: DKIM signs on your From domain (or a subdomain you control), at 2048 bits when available, and the selector resolves in DNS before you raise volume.
Your ESP usually hands you the CNAME or TXT records. Add them, wait for DNS, then confirm with the free DKIM checker before the next big campaign.
Once SPF and DKIM resolve, run the deliverability checklist so a broken PTR, TLS, or unsubscribe header does not undo the DNS work.
DMARC: policy, reports, and alignment
DMARC (Domain-based Message Authentication, Reporting and Conformance) does two jobs. It tells receivers what to do when SPF and DKIM both fail for your domain, and it sends you aggregate reports so you can see who is sending as you.
To pass DMARC, at least one of SPF or DKIM must pass with alignment to the visible From domain. Relaxed alignment (organizational domain match) is acceptable under Google and Yahoo bulk rules.
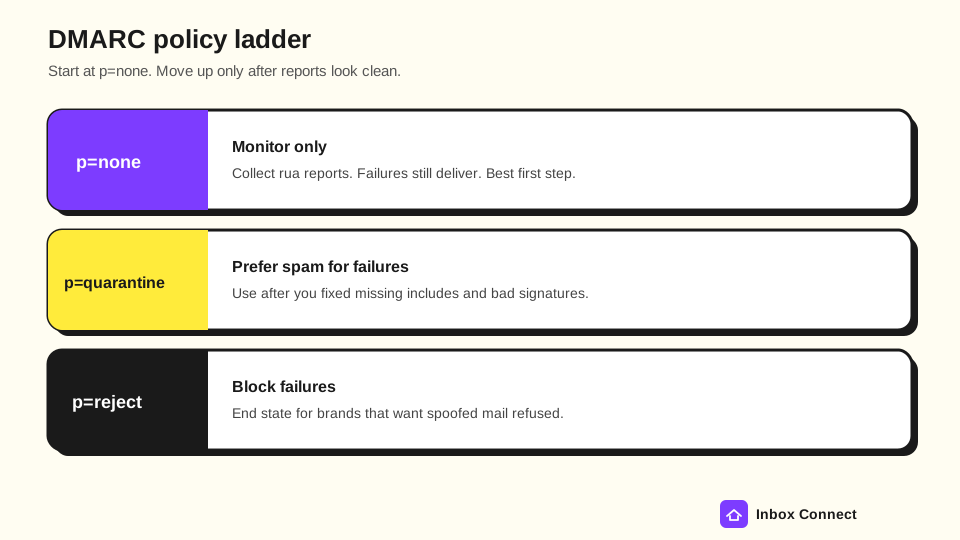
DMARC policy levels
| Policy | What receivers do | When I use it |
|---|---|---|
p=none | Monitor; do not block | First publish; gather reports |
p=quarantine | Prefer spam for failures | After you fixed missing senders |
p=reject | Refuse failures | Clean reports; brand wants hard block |
A starter record looks like this:
v=DMARC1; p=none; rua=mailto:dmarc@yourdomain.com; adkim=r; aspf=r
That says: monitor only, email aggregate reports to this mailbox, and use relaxed DKIM/SPF alignment. After two to four weeks of clean reports, move toward quarantine, then reject when you are ready.
Weak vs strong DMARC posture
Weak: No _dmarc record at all, or a jump from nothing straight to p=reject the same afternoon. Legitimate tools you forgot then bounce while you scramble.
Strong: p=none with a working rua inbox first. You review reports, fix includes and signatures, then raise policy on purpose.
Pro tip: Use the free DMARC checker after every DNS edit. Confirm the policy string you think you published is the one resolvers actually return.
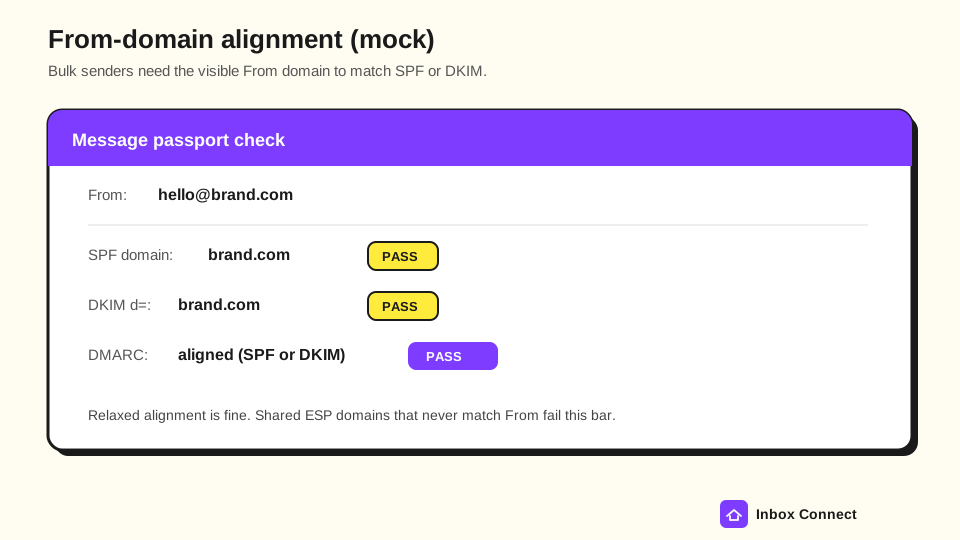
Alignment is the quiet failure mode I see most. SPF can pass on a return-path subdomain while the visible From never matches, so DMARC still fails.
Sign DKIM on the From domain (or align SPF to it) and the bulk-sender bar clears.
BIMI after enforcement
BIMI (Brand Indicators for Message Identification) is not a fourth authentication protocol. It is a logo display path that some inboxes honor only after DMARC is already at p=quarantine or p=reject.
It does not improve placement by itself.
Gmail will not show the mark without a Verified Mark Certificate (VMC) or a Common Mark Certificate (CMC). Yahoo and a few others may show it with weaker requirements.
The record lives at default._bimi.yourdomain.com. Do not publish BIMI on p=none, because providers ignore it until enforcement is real.
Once you are at enforcement, the free BIMI generator builds the record and the BIMI checker confirms it resolves.
How to set up authentication step by step
You can do this yourself if you are comfortable editing DNS. If you are not, have someone who is verify before you flip DMARC past p=none.
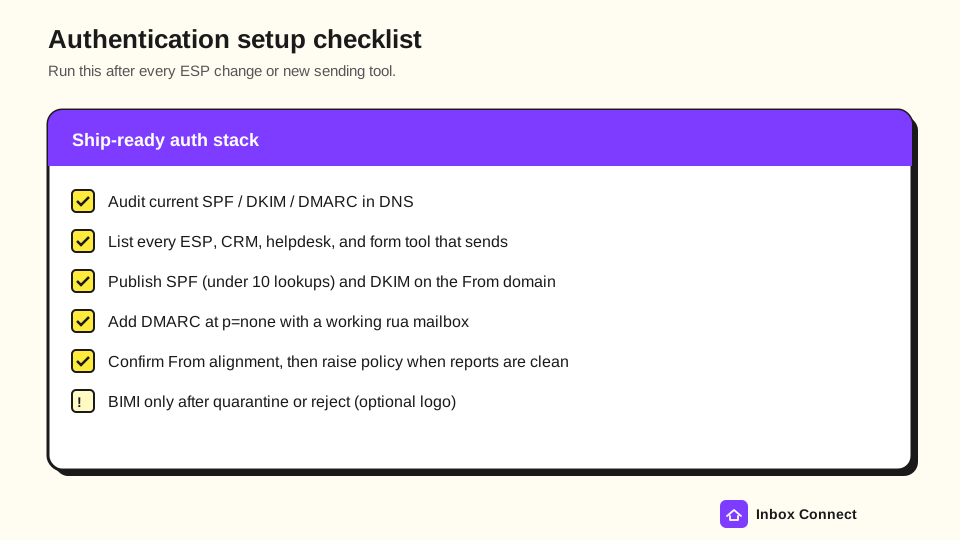
Step 1: Audit what is live now
Look up the current SPF, DKIM selectors, and _dmarc TXT. I still find includes from ESPs clients stopped using three years earlier.
Step 2: Inventory every sender
List your ESP (Klaviyo, Mailchimp, and so on), CRM, helpdesk, invoicing, booking tools, survey platforms, and any other automated mail. Miss one and that stream fails while campaigns pass.
Step 3: Publish or fix SPF
Build one record with every current include and stay under 10 lookups, or start from the free SPF generator.
Soft-fail (~all) is safer while you ramp; hard-fail (-all) comes later when you are sure.
Step 4: Turn on DKIM for your domain
Add the ESP's DKIM records for the From domain, preferring 2048-bit keys when available. Confirm the selector resolves before you send volume.
Step 5: Publish DMARC at p=none
Add _dmarc with a real rua mailbox you will read (the free DMARC generator builds the string). Watch reports for two to four weeks, fix surprises, then move to quarantine and eventually reject.
Step 6: Optional BIMI
Only after enforcement. Host an SVG Tiny P/S logo, add a VMC or CMC if Gmail is the goal, then publish default._bimi.
Step 7: Re-check on a cadence
Authentication is not set-and-forget. Every new tool or ESP migration needs a DNS pass.
I put a quarterly reminder on the calendar and re-run the SPF checker plus DMARC checker after changes.
DNS usually propagates within 24 to 48 hours. Trust recovery at providers can take longer if reputation was already bruised.
Common mistakes I still see
Too many SPF lookups. Each nested include: counts. Flatten or cut dead vendors before you add another SaaS.
Jumping straight to p=reject. That is couch-to-marathon energy. Start at p=none, fix reports, then escalate.
Forgetting subdomains. Marketing and support subdomains need their own SPF/DKIM story, or a deliberate DMARC subdomain policy (sp=).
Skipping warmup on new infra. Perfect auth on a cold dedicated IP still looks like a spam cannon if volume spikes. See email warmup for the paced path.
Ignoring DMARC reports. The XML is ugly. The signal is gold: shadow IT tools, forwarders, and real spoof attempts show up there.
Assuming auth fixes everything. Bad content, dirty lists, and high complaints still fold you to spam. Pair this guide with how to prevent emails from going to spam when you need a step-by-step spam diagnosis.
Pro tip: After any ESP migration, send a seed test to Gmail and Yahoo, then read authentication results in the headers before you congratulate the team.
FAQ
What is the difference between SPF and DKIM?
SPF checks whether the sending server is authorized for the domain. DKIM checks a cryptographic signature so receivers know the signed content was not altered and came from a holder of your private key.
You want both live.
Do I really need all three for bulk mail?
Yes for bulk senders under Google and Yahoo rules. Google requires SPF and DKIM plus a DMARC record (even p=none) when you send more than 5,000 messages per day to personal Gmail accounts.
Yahoo's bulk practices match that stack, and my breakdown of Google and Yahoo bulk sender requirements lists every rule. Smaller senders still benefit from all three.
Will authentication alone fix spam folder problems?
It fixes authentication-related failures and spoofing risk. It will not rescue a dirty list, a 0.3%+ spam complaint rate, or irrelevant blasts.
Fix DNS first, then reputation and engagement.
How long until DNS changes help?
Most DNS edits resolve within 24 to 48 hours. Inbox placement can take days to weeks to reflect cleaner authentication if reputation was already weak.
Can I set this up without a developer?
If you can edit TXT and CNAME records at your DNS host, yes. Most ESPs publish exact steps.
Have a second pair of eyes review before you move DMARC past p=none, because a bad reject policy can bounce real mail.
What happens if I skip DMARC?
Bulk mail to Gmail and Yahoo may fail their sender requirements. You also get no aggregate view of who is sending as your domain, including attackers.
Final Thoughts
You came here to understand email authentication, and you now have the full stack: SPF lists approved senders, DKIM signs the message, and DMARC sets policy plus reporting with From-domain alignment. That is the passport Gmail and Yahoo expect before they trust bulk mail in 2026.
Next step: run the domain scanner on your sending domain, fix any Fail with the DMARC checker and SPF checker, then publish or raise DMARC only after reports look clean. When auth is green, move to my guide on how to improve email deliverability and avoid spam for reputation and engagement.
If you'd rather have a second pair of eyes on it, the paid Email DDx audit and fix reviews your Klaviyo account and gives you a ranked list of fixes.
Russ